Zero-Trust Architecture for Michiana SMBs
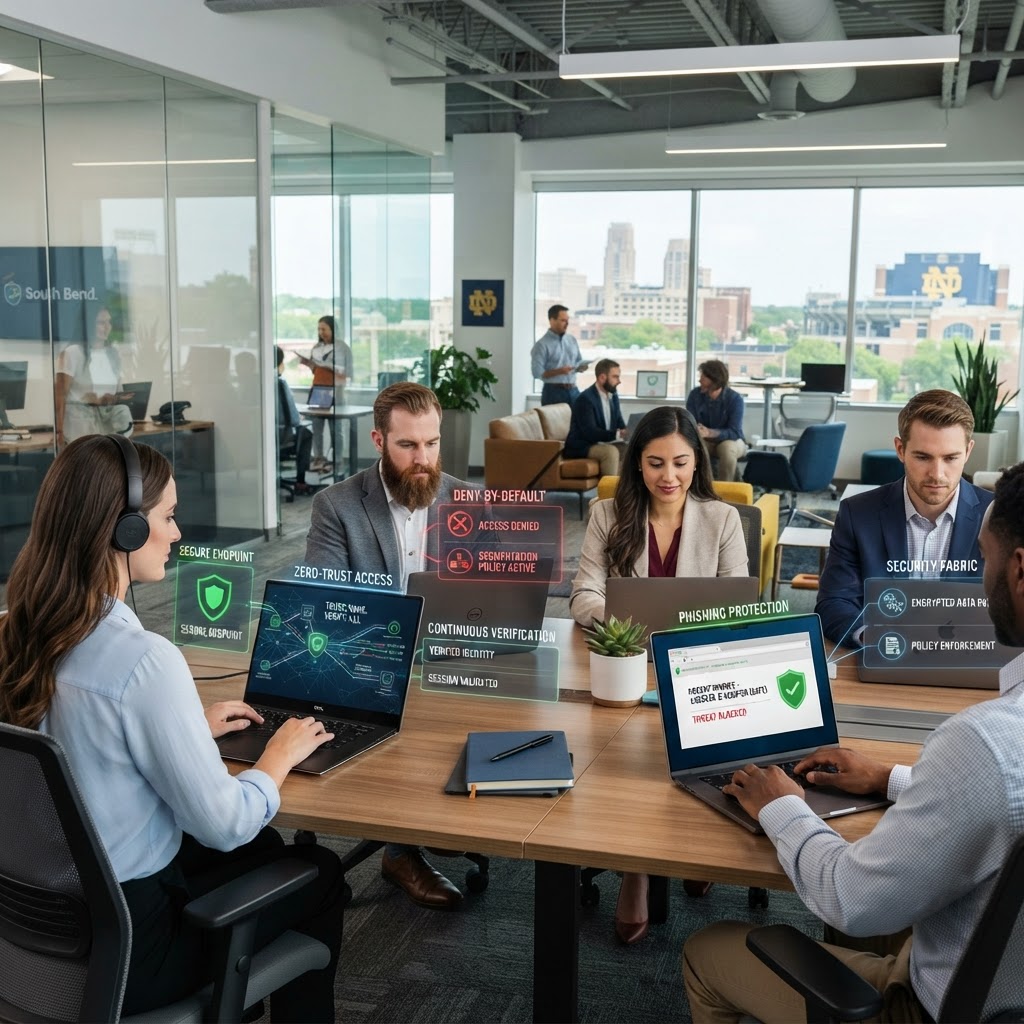
Why Zero-Trust Matters for Michiana SMBs
For small and midsize businesses in Michiana, cybersecurity is no longer just about blocking spam or installing antivirus software. Today’s attackers are using AI to create more convincing phishing emails, fake login pages, and even impersonation attempts that can trick employees faster than ever. Whether you run a manufacturing company in South Bend, a healthcare office in Mishawaka, or a professional services firm anywhere across the region, the risk is real: one successful phishing attack can lead to ransomware, data loss, downtime, and major financial damage.
That is why more organizations are turning to zero-trust architecture. Instead of assuming users or devices inside your network are safe, zero trust follows a simple principle: never trust, always verify. For Michiana SMBs, this approach can be especially effective against AI-accelerated phishing threats because it limits what attackers can do even if they manage to steal credentials. With deny-by-default policies and continuous verification, businesses can build stronger protection without making day-to-day operations unmanageable.
How Zero-Trust Architecture Stops AI-Driven Phishing
Traditional security models often assume that once someone logs in or connects to the company network, they can be trusted. That assumption is exactly what modern phishing campaigns exploit. If an employee clicks a fake Microsoft 365 login page and enters their password, an attacker may gain access that looks legitimate on the surface.
A zero-trust security model helps reduce that risk by requiring verification at every stage. Access is granted based on identity, device health, location, behavior, and the specific resource being requested. In practice, that means a stolen password alone should not be enough to open the door.
For example, a South Bend business using zero-trust architecture might require:
- Multi-factor authentication for every cloud application
- Device compliance checks before access is allowed
- Limited access to files and systems based on job role
- Session monitoring to flag unusual behavior in real time
This approach is powerful because AI-powered phishing is designed to bypass human judgment. Zero trust adds technical guardrails that help prevent a single mistake from becoming a company-wide incident.
The Role of Deny-by-Default Policies
One of the most practical parts of zero-trust architecture for SMBs is the use of deny-by-default policies. Rather than allowing broad access and trying to block only known threats, deny-by-default starts from the opposite position: no user, device, or application gets access unless it is specifically approved.
That may sound strict, but it is one of the best ways to contain phishing fallout. If an attacker compromises one account, they should not automatically gain access to shared drives, financial systems, customer data, or admin tools.
Here are a few deny-by-default steps Michiana businesses can take:
- Limit access by role: Employees should only have access to the apps and data they need to do their jobs.
- Restrict admin privileges: Administrative rights should be tightly controlled and used only when necessary.
- Block unknown devices: Personal or unmanaged devices should not connect to sensitive systems without approval.
- Control application access: Only approved software and cloud services should be allowed.
For many SMBs, this is a major improvement over older “open unless blocked” environments. It is also a practical way to strengthen compliance, reduce insider risk, and improve visibility across the business.
Why Continuous Verification Is Essential
Cyber threats do not stop after login, and your defenses should not either. Continuous verification means checking trust signals throughout a session, not just at the moment a user enters a password. This is especially important against AI-enhanced phishing because attackers can move quickly once they gain access.
Continuous verification may include monitoring for signs such as:
- Logins from unusual locations or impossible travel events
- Access attempts outside normal business hours
- Devices that fall out of compliance
- Unexpected downloads, file sharing, or privilege escalation
If something changes, the system can respond automatically by requiring additional authentication, limiting access, or ending the session. For SMBs in Michiana, this creates a more resilient cybersecurity posture without requiring a large internal IT team.
A good managed IT and cybersecurity partner can help set these controls in a way that balances security with productivity. The goal is not to frustrate employees. It is to make sure access stays appropriate, verified, and aligned with current risk.
Practical Steps to Start Zero Trust in a Small Business
You do not need to rebuild your entire IT environment overnight to benefit from zero trust. In fact, the best zero-trust architecture strategy for most small businesses starts with a few high-impact changes.
Start with these practical steps:
- Turn on multi-factor authentication everywhere for email, cloud apps, VPNs, and admin accounts.
- Review user permissions and remove unnecessary access, especially shared accounts and legacy privileges.
- Segment critical systems so sensitive data and line-of-business applications are not exposed to every user.
- Enforce device management to make sure laptops, desktops, and mobile devices meet security standards.
- Use conditional access policies that evaluate user identity, device status, and risk before granting access.
- Train employees regularly to recognize phishing, impersonation attempts, and suspicious login prompts.
- Monitor and respond continuously using tools that detect unusual behavior early.
For businesses in South Bend and across Michiana, these steps can provide meaningful protection against modern phishing attacks without creating unnecessary complexity. The key is to treat cybersecurity as an ongoing process, not a one-time project.
If your business wants to reduce phishing risk, improve access control, and build a stronger security foundation, The K.A.B. Group can help. Our team works with Michiana SMBs to implement practical cybersecurity solutions, including zero-trust architecture, deny-by-default policies, and continuous verification strategies that fit real business needs.